Real-Time Threat Detection
Process security event streams, detect threats, and investigate information security incidents.
common attack scenarios.
incident response.
disruption to operations.
Searchinform SIEM – Detect Threats Early and Respond Faster
Centralizes, normalizes, and analyzes security data to support incident detection and forensic investigations.
-

Ingests logs from diverse sources
Collects and centralizes security data from endpoints, servers, network devices, and applications, enabling analysis within a single interface.
-

Normalizes security data
Standardizes incoming data into a unified format and enriches it with additional context for more accurate analysis and detection.
-

Correlates events to detect threats
Applies correlation rules to identify patterns, detect threats, and reveal security incidents based on related events.
-

Alerts and enables incident response
Automatically notifies security teams about incidents and provides the information needed for investigation and response.
Key Challenges SearchInform SIEM Addresses
Security data is fragmented
Logs and security events are distributed across multiple systems, limiting visibility and making it difficult to detect threats.
Insider risks are hard to detect
Suspicious user activity is difficult to identify without event correlation, context, and clear risk indicators.
Alert overload reduces visibility
Too many false positives overwhelm security teams and make it harder to identify real threats.
SIEM solutions are complex to deploy
Long implementation cycles and complicated configurations delay adoption and increase operational burden.
Threats are detected too late
Without real-time correlation, suspicious activity goes unnoticed until incidents escalate.
Limited security resources
Small and mid-sized organizations need effective monitoring and threat detection without expanding security teams or adding complexity.
Insufficient event context
Without enrichment and correlation, security events lack the context needed for accurate analysis and response.
Incident investigations are slow
Manual analysis across multiple systems delays response and increases the impact of security incidents.

Searchinform SIEM Detects and Reveals

Malware Activity and Infections
Detects malware outbreaks, virus activity, and signs of system compromise.
Infrastructure and Configuration Issues
Detects hardware misconfigurations, system errors, and abnormal operating conditions.
Unauthorized Access Attempts
Identifies login anomalies, password attacks, and attempts to access restricted data.
Virtual Environment Events
Monitors virtual machines, snapshot activity, and unauthorized changes in virtual environments.
Suspicious User Behaviour
Analyze user activity to quickly understand what happened, who was involved, and how incidents unfolded.
Unauthorized Device Connections
Identifies connections of unapproved devices and changes in IT infrastructure.
Critical Data and Policy Changes
Detects changes to critical files, security policies, system settings, and access permissions.
Security System Failures
Detects failures in protection systems and critical errors in IT systems.Advantages and Benefits of Searchinform SIEM
From threat detection to incident response – all in one integrated platform.

Rapid Deployment
Launch the system quickly with minimal pre-configuration and start detecting threats immediately after installation.

No SIEM Expertise Required
Use an intuitive interface and a built-in correlation rule constructor without advanced SIEM skills.

Optimized for SMEs
Deploy enterprise-level monitoring with moderate hardware requirements and a cost model suited for SMEs.

Low Hardware Requirements
Run SIEM with lower hardware demands than many competing solutions, reducing infrastructure costs.

Node-Based Licensing
Licensing is based on data source nodes – network assets identified by hostname or IP address.

Faster Incident Investigation
Correlate events across systems to quickly identify root causes and reduce response time.

SIEM and DLP in One Platform
Combines SIEM with SearchInform DLP for end-to-end security control.

Experienced Vendor Support
Receive deployment and configuration support from a vendor with 20+ years of information security experience.

Built on Customer Experience
Developed using insights from thousands of implementations across industries and real security use cases.
Learn more about SearchInform SIEM in a brief White Paper.

Gain Full Visibility Across Your IT Infrastructure
Monitors security events across IT systems, correlates them to detect incidents, and supports faster response and forensics.
Network Security Systems
Firewalls, network devices, and traffic monitoring tools.
Virtualization Environments
Virtual machines and virtualization infrastructure components.
Endpoints and Operating Systems
Servers, workstations, PCs, Active Directory, OS.
Business Applications and Databases
Enterprise applications and database systems.
Security Tools
Antivirus software and other protection systems.
Email Servers
Mail servers, mail gateways, and messaging infrastructure.SIEM Ensures Compliance with Major International and Regional Frameworks


27001

Standard

DCC

NIA

18-07
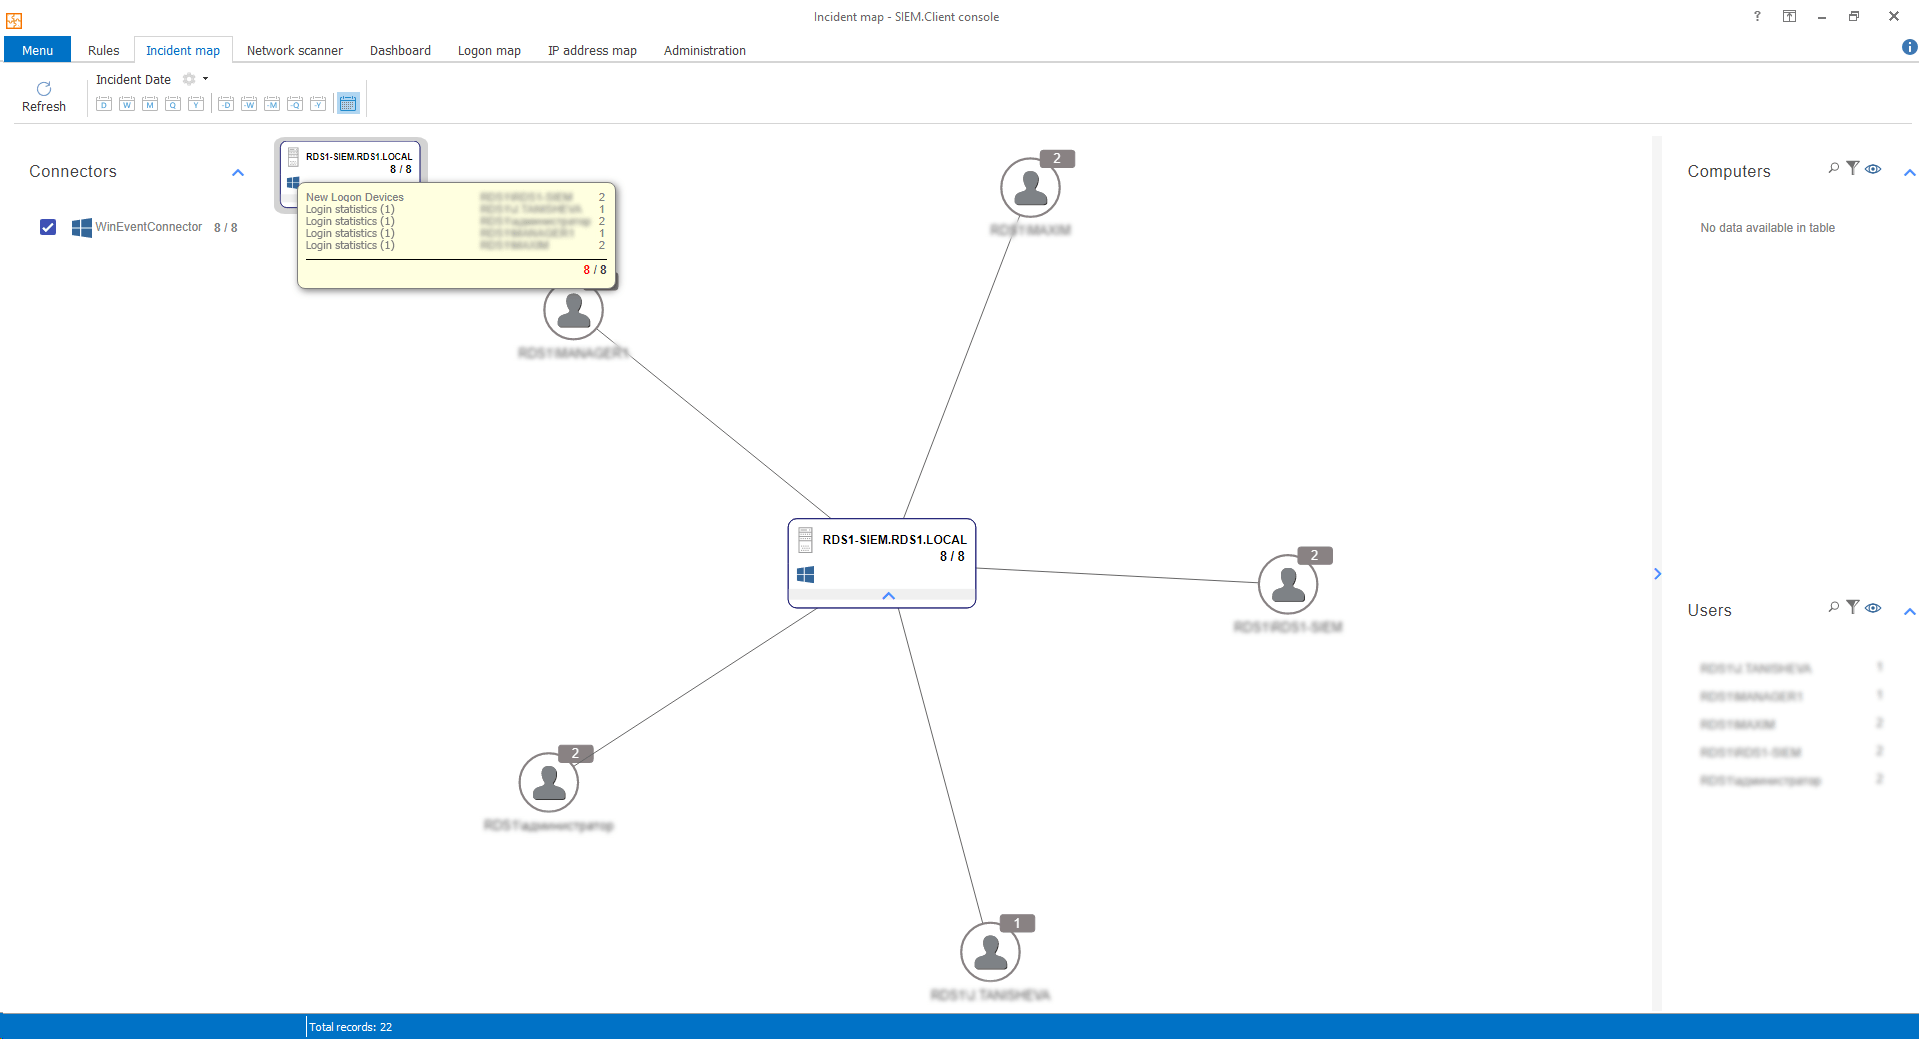
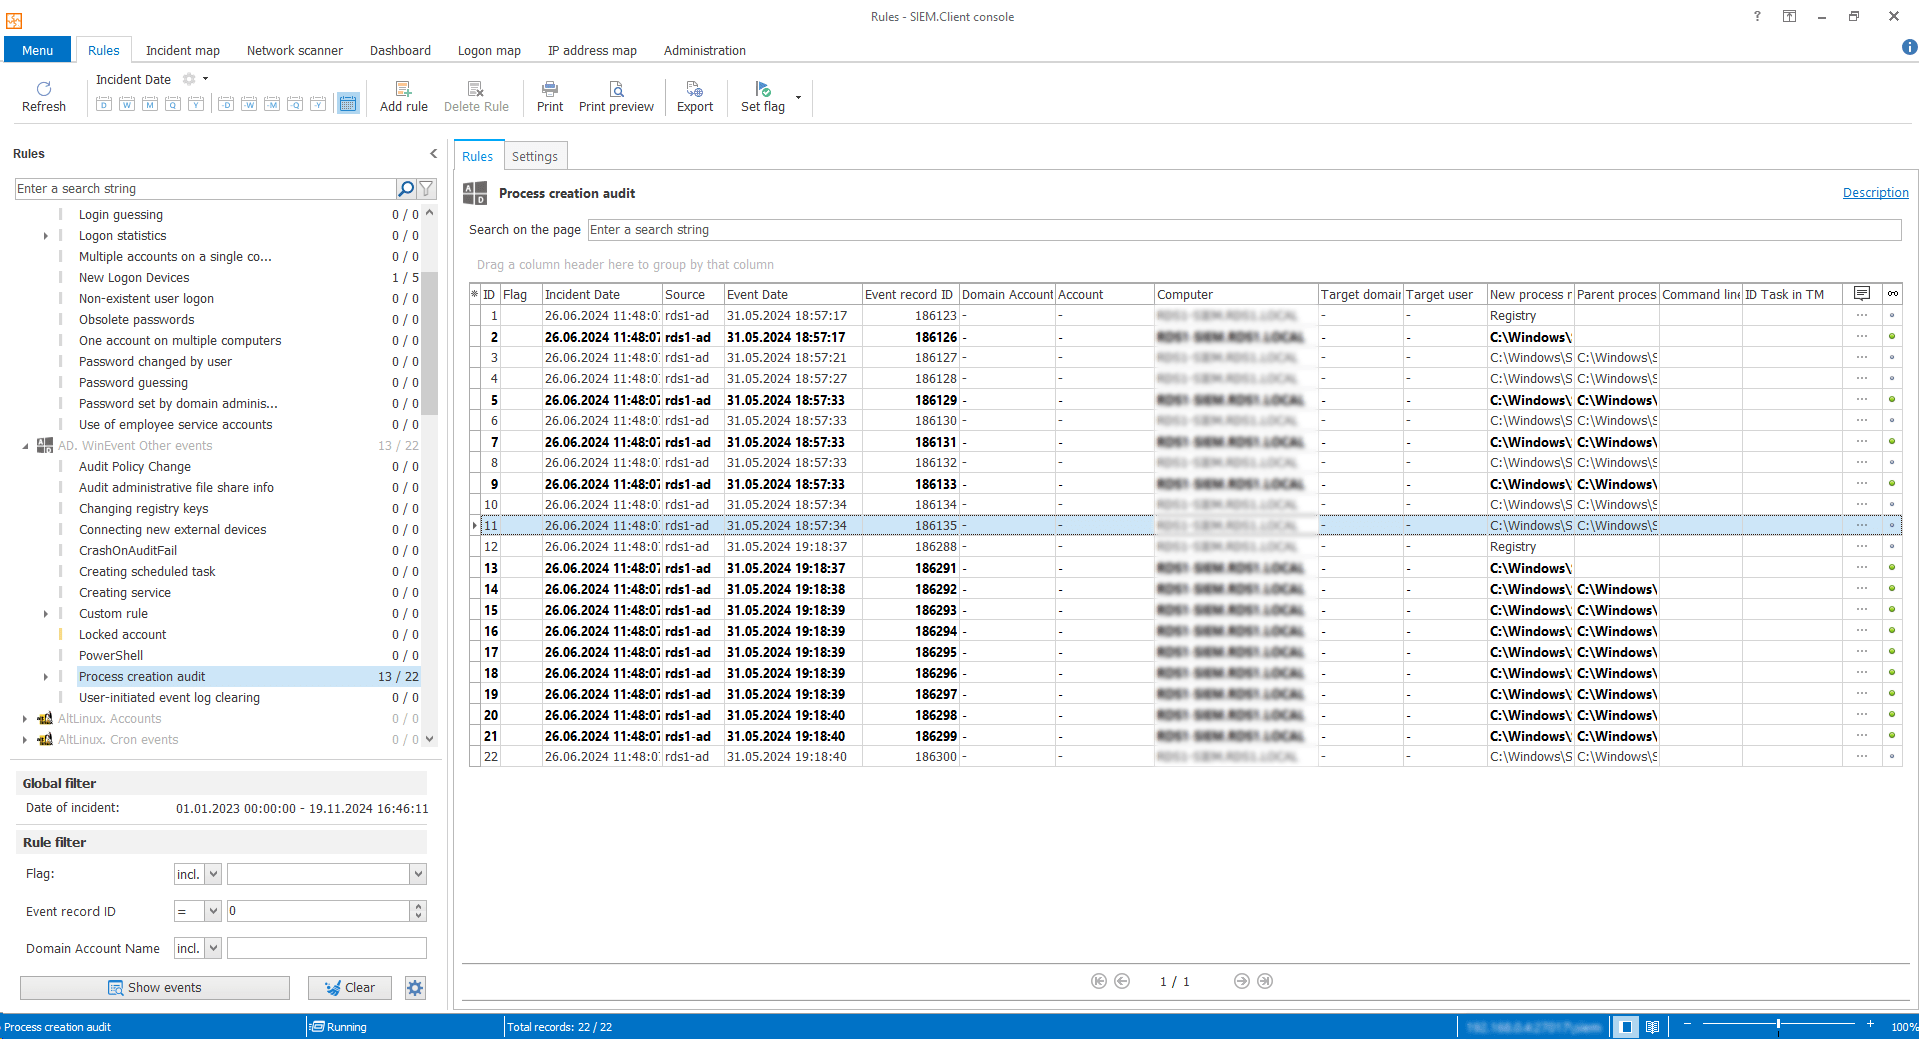
Everything in a Single Interface
Monitor event streams, apply correlation rules, and investigate security incidents in real time.


Frequently Asked Questions
You can see the first results within a day of deployment, with setup completed in hours and no special training required.
Yes, SIEM supports both models, on-premises and cloud deployments.
SIEM has minimal impact on network and system performance thanks to its single-agent architecture.
Yes, it supports common log formats and integrates with SOAR, DLP, identity providers.
Yes. Agents continue working offline and synchronize data when the connection is restored.
Gartner Peer Insights
and customer reviews

 5.0
Powerful DLP with advanced employee monitoring & strong visibility
“We implemented Risk Monitor as a DLP system, but we gained much more, a comprehensive solution for employee monitoring and operational efficiency.”

Why SearchInform
in 22 countries.
representative locations.

SearchInform develops insider risk management and data protection solutions trusted by businesses, manufacturers, financial institutions, and government organizations worldwide. For over a decade, we have helped organizations prevent data theft, reduce human-factor risks, meet compliance requirements, and strengthen internal security controls.
Recognized by Gartner and The Radicati Group, SearchInform delivers a unique single-agent security platform that combines data loss prevention, user activity monitoring, and sensitive data discovery and classification in one ecosystem – reducing complexity, infrastructure load, and deployment costs.
Searchinform clients